Threat Intelligence
PHP2Shell: Patch PHP, Then Keep Testing
PHP2Shell is two critical PHP RCE flaws (CVE-2026-109618 and CVE-2026-109619). The versions that fix them, and why to keep testing after you patch.
Read article
Reproducible labs, security analysis and product updates. Explore the evidence, understand the limits and try the methods yourself.
PHP2Shell is two critical PHP RCE flaws (CVE-2026-109618 and CVE-2026-109619). The versions that fix them, and why to keep testing after you patch.
Read article15 articles
What goes into a penetration test, why prices vary, and what to ask before you buy. Compare AI pentesting plans from £399 a month.
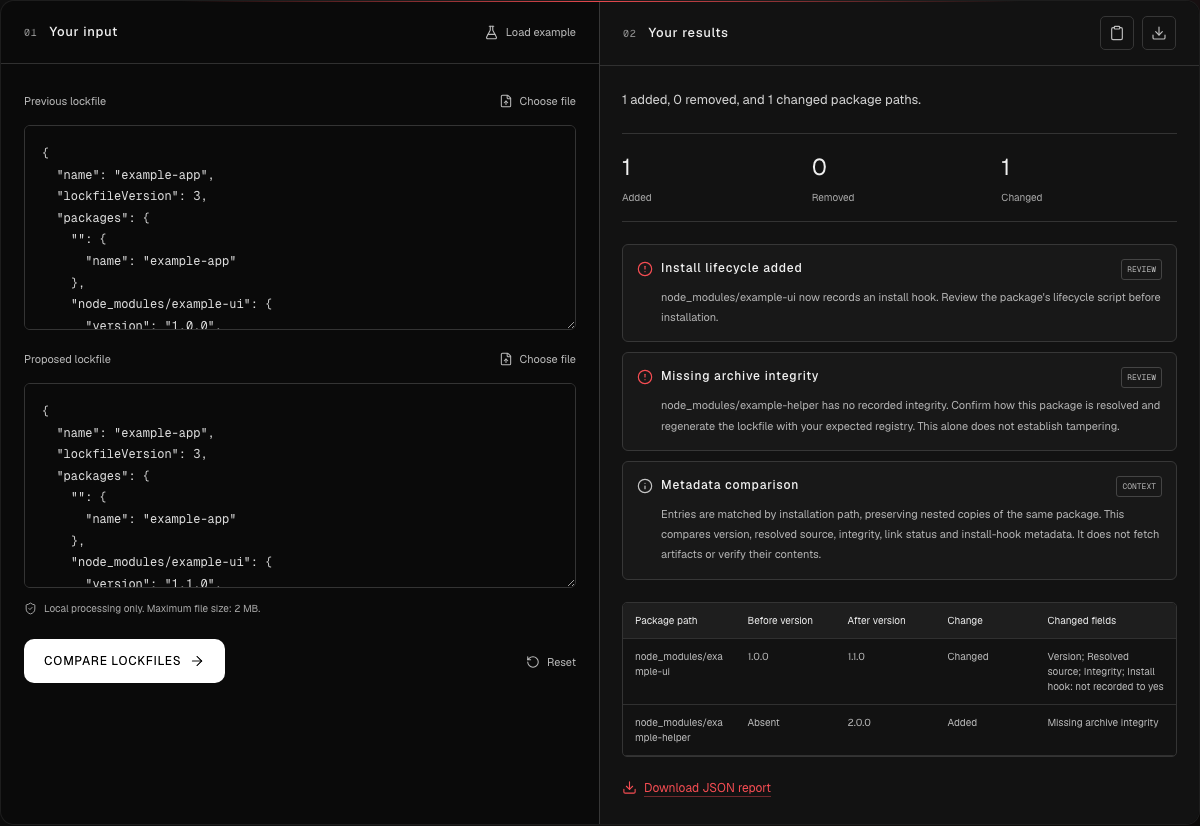
npm lockfile security review: check package sources, install hooks and integrity metadata, then record the evidence behind your merge decision.
Reproduce a supply-chain review with sample npm lockfiles, inspect the evidence, and retest configuration changes using BreachLine's browser tools.
Meet Nebula, the AI security engineer inside BreachLine. Give it a task and follow autonomous security work in one software workspace.
Working exploit vs scanner finding: what enterprise security questionnaires actually accept, and how to turn coverage into adversarial proof.
Researchers found 120 corporate llms.txt files pointing at packages nobody owned. Claude, Codex, and Hermes then installed them inside real networks.
Three flaw clusters turned Cursor, VS Code, and Google Antigravity into a remote-code-execution surface in 2026. How each worked, and how to shut it down.
How an AI security engineer chained DFSCoerce, NetNTLMv1, and DCSync to go from one low-privileged account to Domain Admin, live and fully anonymised.
Evaluate AI browser pentesting with a practical workflow for authenticated sessions, cross-role checks, network evidence and reproducible findings.
TeamPCP poisoned Trivy, Checkmarx, and LiteLLM in a 2026 supply chain campaign (CVE-2026-33634). Who they are, what they hit, and how to stop them.
What Claude Mythos evaluations show about AI pentesting, how they differ from the earlier Opus experiment, and what buyers should verify on their systems.
Compare AI pentesting tools and XBOW alternatives with a practical trial worksheet for scope, authenticated coverage, exploit evidence, retests and cost.
Vercel's April 2026 breach traces to one compromised third-party OAuth token from Context.ai. The full attack chain, the IOCs, and the lessons for your team.
Investigate the Axios npm supply chain attack using affected-version evidence, historical lockfiles, build records and credential exposure checks.
Investigate LiteLLM supply chain exposure with affected-version checks, build evidence, credential scoping and a recovery worksheet for AI teams.