BreachLine Labs / Advisories

Security Advisories

A public record for coordinated vulnerability disclosures. Clear technical context, affected versions and a practical path to remediation.

BreachLine Labs

Published advisories

Our publishing standard
The public record

No advisories published yet.

When a disclosure is ready, you will find the affected versions, supporting references and practical remediation here.

Explore our security research
From the lab

Reproducible exercises are published separately from vulnerability disclosures.

Synthetic supply-chain lab

Follow the evidence. Run the review.

Compare sample npm lockfiles, inspect changed installation metadata and retest registry configuration. The inputs, observations and review steps are available to reproduce.

16 Sep 2026 7 min read

Explore the investigation
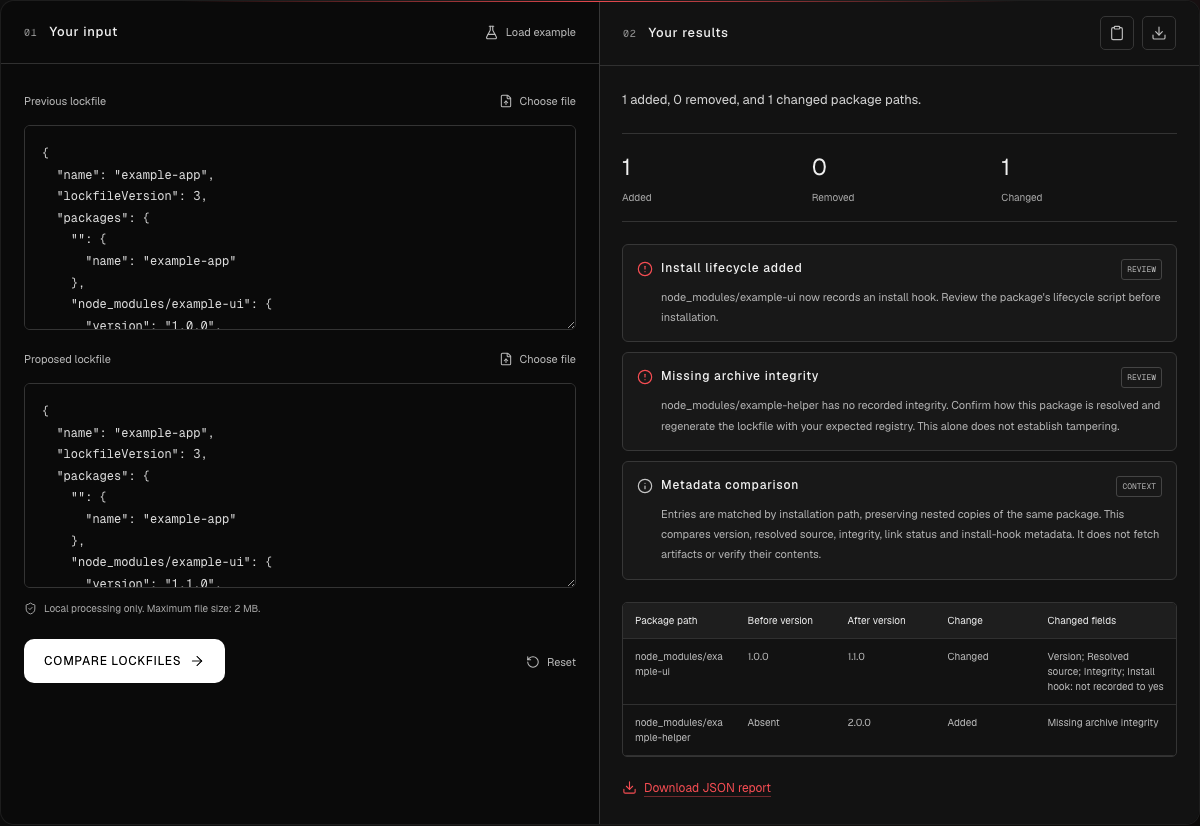
BreachLine lockfile review showing changes in synthetic npm fixtures
Recorded browser output from synthetic fixtures. No package was executed. This exercise is not a vulnerability disclosure or a recorded autonomous agent session.
Our publishing standard

How do we disclose vulnerabilities?

Timelines and coordination

Publication follows review and coordination with the affected party. Fixed versions or available mitigations are dated so discovery, response and publication stay separate.

01

Traceable evidence

A clearly defined product, affected versions and primary references. Technical claims should be reproducible.

02

Coordinated disclosure

Publication follows review and coordination with the affected party. Customer information stays confidential.

03

Useful remediation

Fixed versions or available mitigations, with a dated timeline that separates discovery, response and publication.

Security is a conversation

Report a vulnerability to us

For vulnerabilities affecting BreachLine, start with our disclosure policy or contact the security team.

Explore